
Keeping data forever is not a security strategy
Professional offices accumulate information quickly: client files, employee background checks, tax records, medical information, financial documents, scanned identification, email, cloud files, old computers, removable drives, copiers, phones, and backup media. Keeping everything “just in case” can increase breach impact, complicate discovery, and make secure disposal harder. Deleting too soon can create legal, contractual, operational, or records-retention problems.
A sound disposal program begins with an authorized retention decision and ends with evidence that the selected information and media were handled correctly. It is not the same as emptying a recycle bin, resetting a device, or receiving a vendor invoice marked “destroyed.”
This guide helps Central Florida law firms, accounting practices, medical and dental offices, insurance agencies, property managers, employers, and other professional organizations structure that process. It is general information, not legal or compliance advice. Retention and disposal duties depend on the information, organization, contract, regulator, litigation status, and applicable law.
Know which requirements apply
Different records can trigger different rules. Two federal examples illustrate why classification matters:
- The Federal Trade Commission's Disposal Rule applies to consumer reports and information derived from them when maintained for a business purpose. It requires reasonable and appropriate measures to prevent unauthorized access to or use of that information during disposal. The scope can include employers, landlords, lenders, insurers, mortgage brokers, automobile dealers, attorneys, private investigators, debt collectors, and service providers.
- The HIPAA Rules require covered entities and business associates, as applicable, to protect protected health information through disposal and to address final disposition and reuse of electronic media containing electronic protected health information.
The FTC Safeguards Rule separately includes disposal requirements for covered financial institutions, subject to specified exceptions. Other records may be governed by state law, professional rules, contracts, tax requirements, litigation holds, insurance terms, customer commitments, or internal policy.
Do not apply one destruction schedule to every record. Build a retention matrix that identifies record owner, information type, system, legal or business basis, retention period, hold status, approved disposal method, and required evidence. Have qualified counsel or compliance professionals validate the rules that matter to the organization.
Start with an inventory
Map information across both obvious and overlooked locations:
- File rooms, desks, storage boxes, reception areas, and remote-work locations.
- Laptops, desktops, servers, network storage, phones, tablets, and removable drives.
- Printers, scanners, multifunction copiers, postage systems, cameras, and access-control devices with storage.
- Email, collaboration platforms, cloud drives, backups, archives, and SaaS applications.
- Vendor portals, managed service systems, eDiscovery exports, and data warehouses.
- Development, test, training, and reporting copies.
- Employee-owned devices or media authorized for business use.
For each location, record the information category, sensitivity, owner, system custodian, retention rule, backup relationship, and disposal path. Do not put passwords, encryption keys, or full sensitive records into the inventory.
Decide before destroying
Before approving disposal, verify:
1. The documented retention period has ended.
2. No litigation, investigation, audit, public-records, insurance, contractual, or preservation hold applies.
3. The business owner and authorized records or legal contact approve disposal.
4. Required records have been transferred or preserved in an approved location.
5. Copies, exports, backups, and downstream systems are addressed.
6. The disposal method fits the media and sensitivity.
Use a repeatable approval record. Emergency cleanups and office moves are particularly risky because employees may make fast decisions about boxes and equipment without knowing what they contain.
Match the method to the media
NIST Special Publication 800-88 Revision 2 defines media sanitization as a process that renders access to target data infeasible for a given level of effort. It emphasizes selecting methods based on information sensitivity and media characteristics.
Paper and physical records
Use a method that makes sensitive content unreadable and not reasonably reconstructable. The FTC identifies examples such as shredding, pulverizing, or burning consumer-report information, as appropriate. Ordinary waste or recycling bins are not a secure disposal method for intact confidential records.
Use locked collection consoles, define who can access them, establish pickup procedures, and prevent overfilling. Address labels, notes, photographs, badges, prescription labels, printed emails, and drafts—not only formal files.
Magnetic drives and tapes
Choose a validated clear, purge, or destroy method appropriate to the media, information sensitivity, and reuse decision. A quick format or file deletion may remove pointers without making the underlying information infeasible to recover. Degaussing applies only to suitable magnetic media and can render equipment unusable; it is not an all-purpose method.
Solid-state drives, flash media, and mobile devices
Flash-based storage introduces controller, overprovisioning, wear-leveling, and implementation considerations. Use manufacturer-supported sanitize functions or other methods evaluated for the specific device. If a trustworthy purge cannot be verified and the information risk is high, physical destruction may be appropriate.
Do not assume that drilling one hole, breaking a screen, or performing a consumer factory reset sanitizes every storage component.
Encrypted media and cryptographic erase
Cryptographic erase can be effective when encryption was correctly implemented, keys are securely managed, and the method and media meet the organization's requirements. Verify that all target data was encrypted, copies of keys are addressed, and the implementation matches current guidance. Encryption added only at the end does not retroactively prove that earlier data was always protected.
Cloud and software-as-a-service data
“Delete” can mean soft deletion, delayed purge, removal from the user interface, or scheduled expiration. Ask providers:
- When does data become inaccessible to users?
- When is it removed from active systems and backups?
- Can administrators or support personnel restore it?
- What happens to replicas, logs, exports, archives, and disaster-recovery copies?
- How are customer-controlled encryption keys handled?
- What deletion evidence is available?
- What happens when the contract ends?
Record the provider's documented behavior and contractual commitments. Do not claim immediate destruction if the platform uses a defined retention and purge cycle.
Printers, copiers, and specialized equipment
Multifunction devices and other office equipment may contain drives or flash storage. Include them in asset inventories, lease-return procedures, vendor contracts, and disposal reviews. Confirm who owns the storage component and what occurs before resale, return, repair, or recycling.
Reuse requires its own decision
A device reassigned to another employee, donated, returned to a lessor, sold, or sent for repair may expose data even though it is not being thrown away. HHS guidance distinguishes final disposal from media reuse and requires covered entities to remove electronic protected health information before media is made available for reuse.
Before reuse:
- Confirm data preservation requirements.
- Remove organizational accounts, management profiles, tokens, and certificates.
- Apply the approved sanitization method.
- Verify the result.
- Reinstall from trusted media or enrollment processes.
- Reassign the asset in the inventory.
A device that cannot be reliably sanitized should not be donated or resold merely because it still powers on.
Manage disposal vendors as security providers
The FTC notes that due diligence for a document-destruction contractor can include reviewing audits, references, certifications, and information-security practices. Apply risk-based vendor management to electronic-media recyclers and cloud providers as well.
The contract should address:
- Scope, media types, locations, and approved methods.
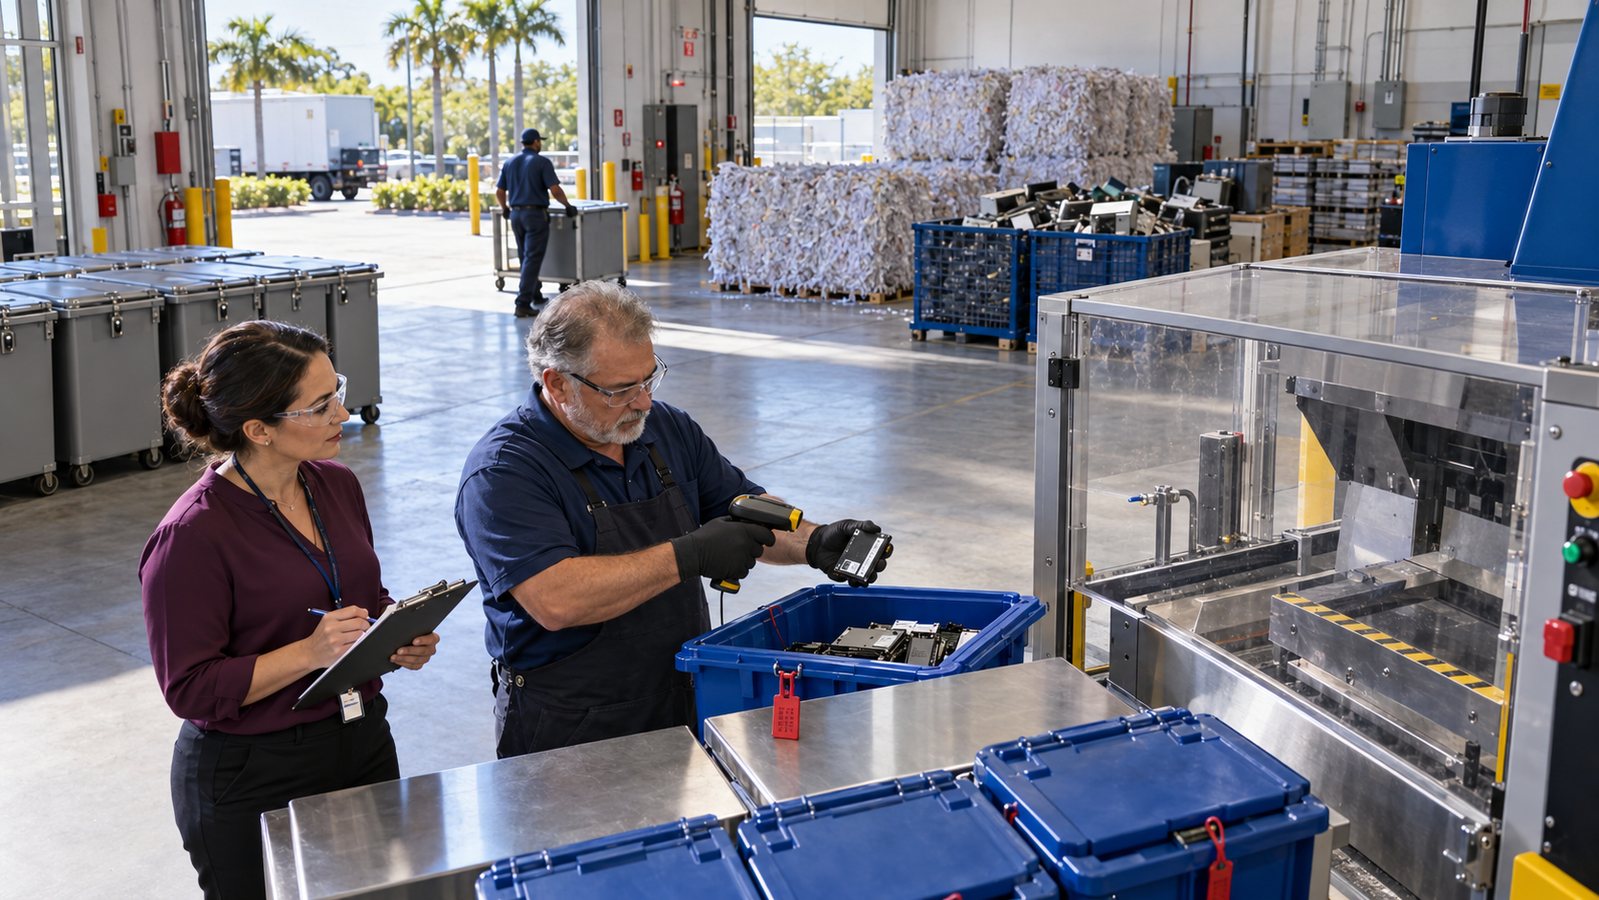
- Secure collection, transportation, storage, and chain of custody.
- Personnel screening and access controls where appropriate.
- Subcontractors and downstream processors.
- Incident notification and cooperation.
- Certificates or detailed records of sanitization or destruction.
- Audit rights or other evidence of performance.
- Return, reuse, resale, and residual-value handling.
- Final disposition and environmental requirements.
A certificate is useful evidence, but it does not replace due diligence, correct scope, or verification. Reconcile certificate quantities, serial numbers, dates, and methods with the assets released.
Build an evidence packet
For each disposal event, retain evidence appropriate to risk and policy:
- Approval and hold check.
- Record categories and date ranges.
- Asset identifiers, media type, make, model, and serial number where applicable.
- Selected method and basis for selection.
- Person or vendor performing the work.
- Date, location, and chain-of-custody record.
- Tool, command, device result, or destruction record where relevant.
- Verification result and reviewer.
- Exception, failure, and remediation.
- Vendor certificate matched to the released assets.
Do not include recoverable sensitive content, passwords, or cryptographic keys in the evidence packet. Protect the evidence according to its own retention and access requirements.
A quarterly disposal review
Once each quarter, a professional office can review:
- Records past retention that are not under hold.
- Devices awaiting repair, return, reuse, recycling, or destruction.
- Closed client or employee files in paper and electronic systems.
- Inactive cloud accounts, exports, archives, and shared links.
- Backup retention that no longer matches policy.
- Vendor certificates that have not been reconciled.
- Exceptions with no owner or completion date.
- Changes in law, contracts, systems, or business needs.
Report counts and unresolved risks to leadership without exposing the sensitive records themselves.
Common mistakes to avoid
- **Deleting without checking holds.** Retention and preservation decisions come before sanitization.
- **Assuming recycle bin means destroyed.** Logical deletion may leave recoverable data.
- **Ignoring cloud and backup copies.** The visible record may be only one instance.
- **Using one method for every device.** Media technology affects effective sanitization.
- **Trusting a factory reset without validation.** Confirm what the device and management platform actually erase.
- **Losing chain of custody.** Secure handling matters before final destruction.
- **Accepting an unmatched certificate.** Reconcile evidence to the specific assets and scope.
- **Keeping everything indefinitely.** Unnecessary retention increases exposure and operational cost.
A defensible disposal program connects retention authority, inventory, method selection, controlled execution, verification, and evidence. If a Central Florida professional office can show those six elements, it is better prepared to protect clients, patients, employees, and the business throughout the information lifecycle.
Human-reviewed draft. This article provides general information, not legal, records-management, healthcare, financial-services, or compliance advice.